


Local AI for professional secrecy holders: process client and patient data inside your own network
Law firms, practices, hospitals and notaries want to use AI without handing secrets protected by Section 203 StGB to external AI services. We bring models and knowledge into your controlled environment, document data paths, permissions and operations and, on request, the people involved accept a written secrecy obligation.
Companies worldwide trust WZ-IT























What blocks AI for professional secrecy holders today
External AI services process client, patient or other confidential data through additional involved parties.
A DPA addresses the GDPR layer but does not alone settle necessity, secrecy obligations and the access chain under §203.
Models, knowledge sources, logs, backups and remote maintenance together form the actual data path.
In a managed service, contributing persons and any further participants must also be effectively bound to secrecy.
Local AI for GDPR and Section 203 requirements
We configure and operate the local AI platform for the agreed GDPR and Section 203 scope, as an AI Cube or on your own infrastructure. This includes controlled data paths, limited permissions, documented maintenance, the appropriate DPA and, on request, written secrecy obligations for the people involved. Legal evaluation of the specific use remains with the controller and its advisers.
What §203 StGB prohibits
§203 StGB protects confidential information entrusted by clients, patients and other parties. The necessary involvement of contributing persons is permitted. What matters is that access is limited to what is necessary, the people involved are bound to secrecy and the complete data and maintenance path is controlled.
Why cloud AI is the problem
With public AI services, inputs and documents leave your own infrastructure. Whether a service is suitable in a specific case therefore depends not only on a DPA, but also on data flows, subprocessors, access permissions and the actual use.
Why local processing helps
On-premises inference, local vector search and internally operated interfaces keep technical processing in your controlled environment. This reduces external data paths and subprocessors and allows access to be limited precisely.
Managed service with a secrecy obligation
When we provide setup or operations as a contributing person, the people involved accept a written secrecy obligation and are instructed about the criminal consequences. Where personal data is involved, this is combined with a DPA, limited administrative rights and documented maintenance paths.
What we deliver for it
These technical and contractual building blocks form part of the agreed §203 scope:
Data-protection layer
Secrecy and instruction on criminal consequences
necessary rights, logging and controlled paths
This content is general information and not legal or tax advice. The specific implementation under §203 must be reviewed professionally on a case-by-case basis.
AI by profession: law firm, practice, hospital and notary
Per profession: starting point, use cases with results and the right operating model.
Law Firm
§203 · Case data · RAG
Case-law research, draft pleadings and case knowledge with local AI configured for a defined Section 203 scope.
Learn moreTax Advisors
§203 · DATEV · Client data
Process documents, correspondence and firm knowledge with local AI configured for a defined Section 203 scope.
Learn moreMedical Practice & MVZ
§203 · Patient data · PMS
Practice knowledge, drafts and documentation with local models in the practice network.
Learn moreHospital & Clinic
§203 · HIS · air-gapped
Doctor's letters, tumour board, coding at volume - air-gapped in your own data centre.
Learn morePsychotherapy
§203 · Therapy data · local
Drafts, professional research and internal knowledge with local models in the practice.
Learn moreNotary
§203 · Deeds · RAG
Deed drafts and register-law research - party data stays in the office.
Learn moreAuditors
§203 · Working papers · RAG
Working papers, IDW PS research, report drafts - client figures stay under your control.
Learn moreAdvise. Build. Operate. From one team.
Sovereign AI is a lifecycle, not a device purchase: advice, build and operations come from one team.
Advise & design
Workshop, sizing, data classification and §203 contract framework. We understand your stack, professional software and compliance requirements before we recommend.
Build & integrate
On-premise build on your hardware, RAG on your documents with access control, integration into your professional software. Plus the DPA and, on request, a written secrecy obligation under Section 203 StGB.
Operate & maintain
Updates, monitoring, model upgrades and RAG upkeep in ongoing operation. For the AI Cube, AI Cube Care runs with the device for the first twelve months and is cancellable monthly after that; handover to your team and knowledge transfer included.
The full service range for your local AI
From hardware and inference through RAG and integration to operations and security - no interface ping-pong between advice, build and operations.
Local AI infrastructure
Knowledge & RAG
Integration & development
Your own hardware, open models, a documented obligation
Your hardware, controlled data flows
On-premise deployment at your site; external integrations, updates and remote access are configured deliberately and documented.
Open source, no lock-in
Ollama, vLLM, Open WebUI, Qdrant - operable internally, no vendor lock-in.
GDPR & §203
DPA and, on request, a written secrecy obligation with instruction of contributing persons about the criminal consequences.
AI Cube for firms, practices and other §203 environments
The local AI platform brings AI chat, knowledge spaces and local models into your network. It is configured for the agreed GDPR and §203 framework; professional-software integrations remain a clearly scoped integration service.
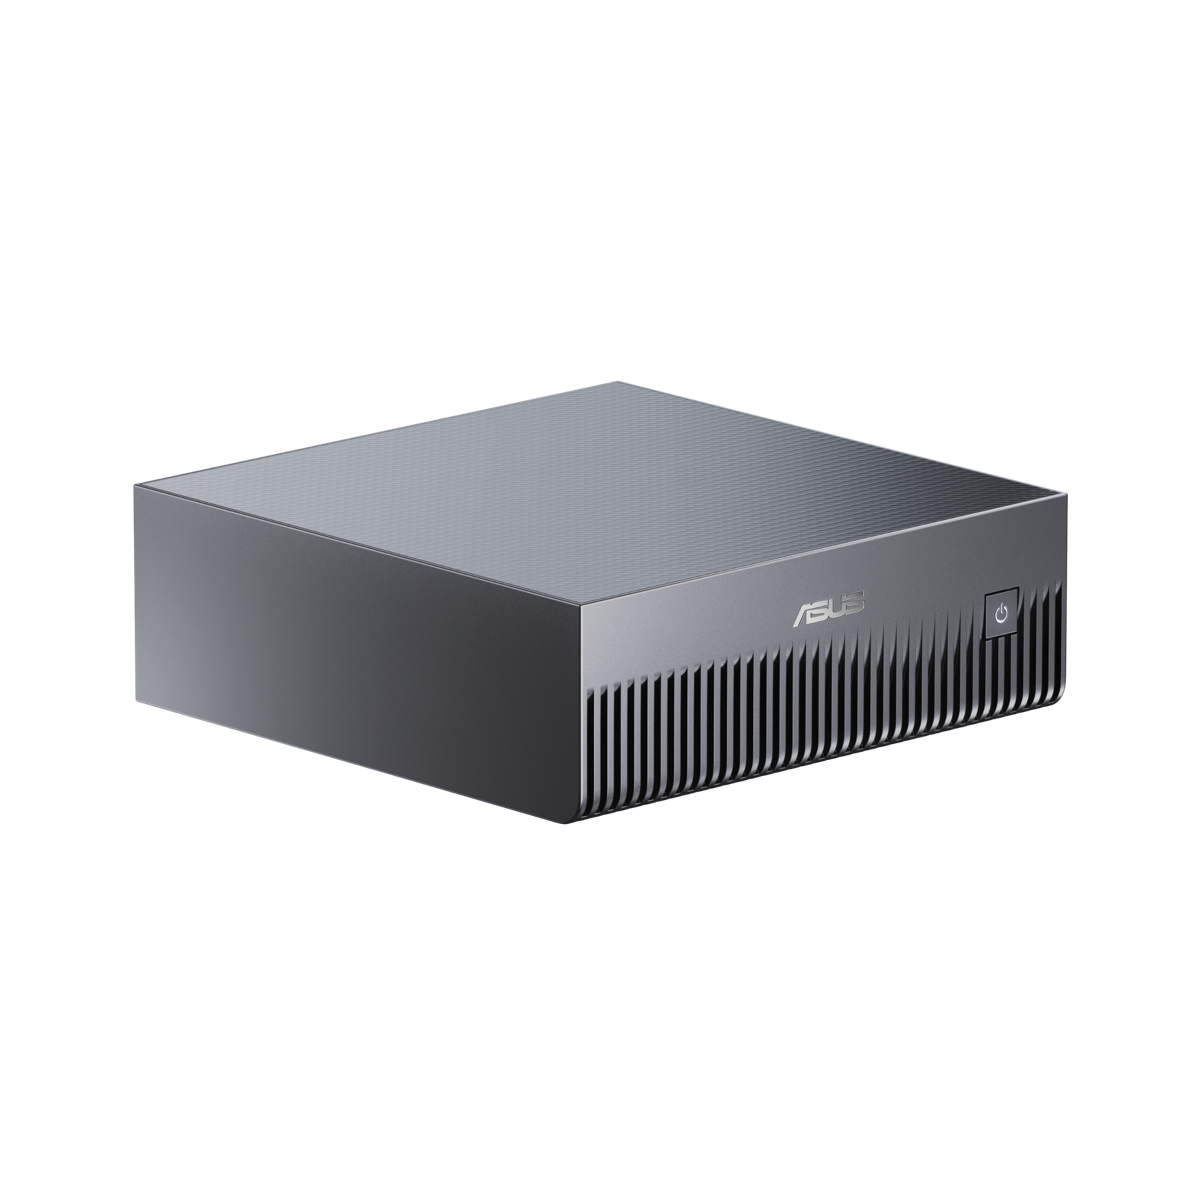
Delivered ready to use within 10 working days
AI Cube
from €6,490 excl. VAT one-time
Device, setup, briefing and shipping
from €349.90 excl. VAT / month
AI Cube Care · first year accompanied, then cancellable monthly
- Compact AI appliance on NVIDIA GB10 with 128 GB unified memory and 1 TB NVMe
- Open WebUI with knowledge bases, groups and roles
- A local language model, a fast model for short tasks and an embedding model
- Hardened system, firewall, HTTPS on the local network
- Remote maintenance through NetBird, logged and switchable
- Handover documentation, a 30-minute briefing and shipping within Germany
- Two-year manufacturer warranty
Expandable when required
RAG, data sources, integrations, secure connectivity and custom workflows are scoped separately.
Operable for the long term
AI Cube Care keeps the device running: a monthly maintenance window, tested model updates with a rollback path, round-the-clock monitoring, ticket support and warranty handling. The data processing agreement under Art. 28 GDPR comes with the order; for confidentiality professionals the written secrecy obligation is available on request under Section 203 (4) of the German Criminal Code, including instruction on the criminal consequences; on request remote access stays switched off by default.
For professional secrecy holders
Connect AI and applications in a Section 203 operating model
In addition to local AI, WZ-IT can operate the related portals, open-source applications, Supabase backends and custom services in a managed cloud designed for professional secrecy holders.
In-depth guides on this topic
Frequently asked questions about AI and Section 203 StGB
Answers to the most important questions
Yes. Section 203(3) StGB permits the necessary involvement of other contributing persons. The specific use needs controlled data paths, an effective secrecy obligation and the other data-protection and profession-specific requirements.
A DPA is an important part of the GDPR layer. For secrets under §203, necessity, involved persons, secrecy obligations, access rights and further providers must also be assessed.
The organisation must define which data may be processed, who receives access and how service providers are involved within the §203 framework.
Server location is only one criterion. Provider identity, subprocessors, access rights, third-country transfers, contracts and the actual processing also matter.
AI Cube costs from €6,490 excl. VAT one-time for the 1 TB version, plus AI Cube Care at from €349.90 excl. VAT / month; the first twelve months run with the device, cancellable monthly after that. Hardware, hardening, an agreed local model, monitoring, updates and support are included. Larger deployments are quoted per project.
A fully local or isolated deployment can be configured. Updates, external models, web search and remote maintenance are then unavailable or require controlled transfer procedures.
Common open-source LLMs (Llama, Qwen, Mistral, Gemma) on NVIDIA hardware - from the AI Cube as a GB10 appliance for a single practice to an RTX GPU server for larger institutions. No vendor lock-in.
IT service providers who contribute to the professional activity can be other contributing persons within the meaning of Section 203(3) StGB; Section 203(4) StGB then also makes their unauthorised disclosure a criminal offence. For WZ-IT this means: we document data paths, roles, technical safeguards and operating responsibility. On request, the people involved accept a written secrecy obligation and are instructed about the criminal consequences; an appropriate DPA is added where personal data is processed.
Enquiry
Assess local AI for professional secrecy holders
Describe the workflow and data that should be processed locally or in a controlled environment.
Let's Talk About Your Idea
Whether a specific IT challenge or just an idea - we look forward to the exchange. In a brief conversation, we'll evaluate together if and how your project fits with WZ-IT.
Arrange a callback
Companies worldwide trust WZ-IT
