


On-premises infrastructure for mid-sized businesses: run locally, managed by WZ-IT
When data must not leave the building, you need systems on site and someone to operate them. WZ-IT supplies and operates the App Node for open-source applications, the AI Cube for local AI and secure connectivity with sites and cloud services.
Companies worldwide trust WZ-IT





When on premises is the right choice for your organisation
Four situations in which applications and data should stay in-house, fully or in part.
The data must not leave the building
Personnel, customer and project data needs to be processed on your own network. Another cloud service is ruled out, while an unmanaged server of your own ties up internal IT.
Professional secrecy under Section 203
Law firms, medical practices, tax advisors and auditors must govern access, remote maintenance, backups and involved service providers in a traceable way, not only the storage location.
Dependent on one cloud provider
When applications and data sit with the provider, the provider decides on pricing, features and export options.
Several sites, one network
Office, other sites, home offices and mobile users need the same systems without internal applications being exposed on the internet.
Two on-premises servers for different workloads
The App Node runs open-source business applications on compact hardware. The AI Cube is designed for local AI models, RAG and concurrent inference; for larger projects we design a custom AI infrastructure. Both are preconfigured and operated by WZ-IT.
Open-source applications
WZ-IT App Node
Compact on-site appliance with hardware, applications, setup and ongoing operations in one managed subscription.
from €349 excl. VAT / month · plus one-time provisioning and initial setup
View App Node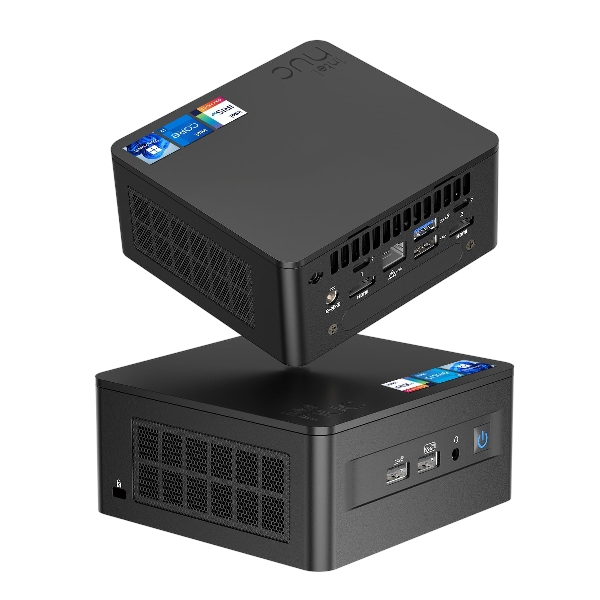
Local AI
AI Cube
On-premises AI node for local AI chat, private knowledge spaces, RAG and production model inference.
from €6,490 excl. VAT one-time · Section 203 scope on request
View AI Cube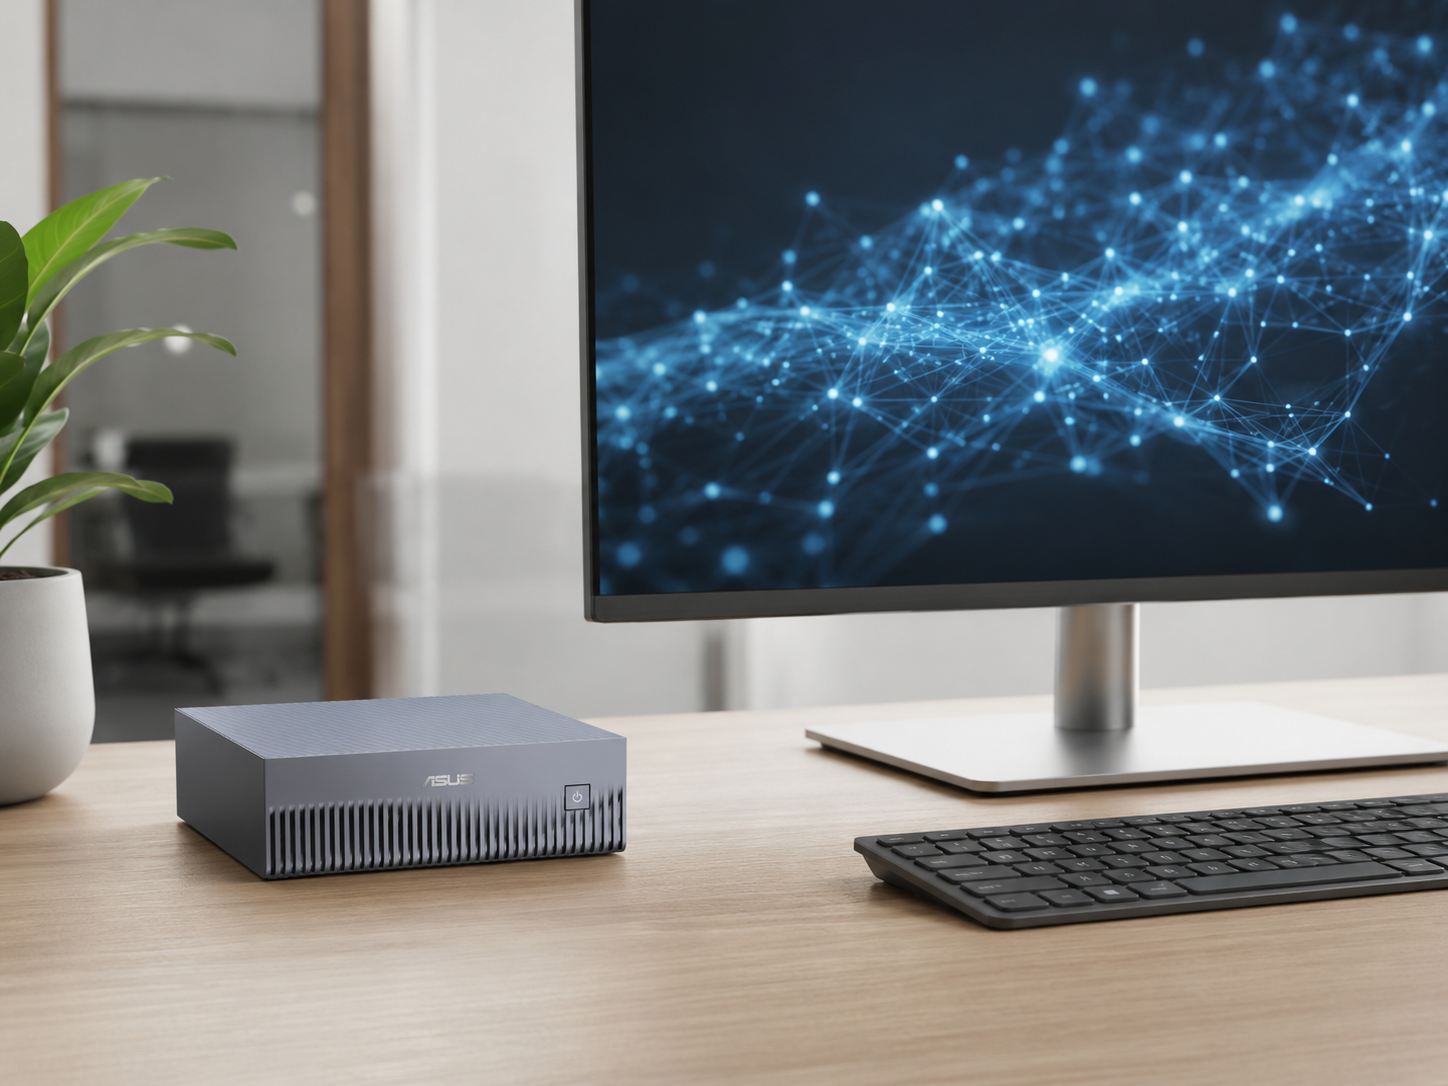
Services for local and hybrid infrastructure
Beyond the products, WZ-IT plans and operates the surrounding environment: access, cloud connectivity and integration.
Site connectivity and secure access
NetBird, WireGuard and existing identities connect sites, home offices and mobile users through defined access paths.
View secure accessHybrid cloud and local systems
Local systems and approved cloud services are connected through defined network, identity and data paths.
Integration and further development
From local AI to custom application integration, WZ-IT develops and integrates beyond standard operations.
View software developmentRun open-source applications on premises
The secured framework can run a range of applications from our open-source portfolio. Resource demand, security requirements, availability and licensing determine which workloads share a node and which remain isolated.
Supabase
Postgres backend with auth, storage, realtime and vector on a fully managed local App Node.
View product pageNextcloud
Sovereign file, collaboration and office platform - the on-premise Microsoft 365 alternative.
View expertisen8n
Automation and workflows in-house - privacy-focused Zapier/Make alternative.
View expertiseMore applications from our open-source catalogue
Typical applications we install, integrate and operate on suitable on-premises hardware. Network and access components such as NetBird or WireGuard are designed separately as part of the architecture.
 Paperless-NGX
 BookStack
 Mattermost
 Vaultwarden
 OpenProject
 Zammad
 Grafana
 Odoo
 Keycloak
 Jitsi
From the initial consultation to on-premises operations
Four steps to operations. The architecture defines how the system is reached: locally, via VPN or in a controlled hybrid setup.
- 1
Initial consultation and inventory
Site, space, power, network, existing servers, applications, users and data volume are recorded.
- 2
Target architecture
The architecture defines which data and functions remain local, which approved services are reachable externally and which connections updates, backups and remote maintenance require.
- 3
Provisioning and setup
Hardware, platform and applications are sized appropriately and preconfigured, with encryption, firewall and secure administration.
- 4
Ongoing operations
WZ-IT handles monitoring, updates, technical administration and support. Responsibilities, service windows and operational boundaries are set out in the agreement.
Architecture
Local, via VPN or in a controlled hybrid setup
The App Node runs at your premises
The agreed applications run on the provided hardware at your organisation. Local users and systems reach them directly over the internal network.
Access aligned with your environment
The node can remain entirely internal. External access is implemented through NetBird, WireGuard, an existing VPN or a secured gateway.
Data flows are defined
Updates, backups, remote maintenance and connected services are deliberately designed before deployment. Required connections and technical measures are documented.
Your data stays in-house, WZ-IT handles operations
The applications run on your network. WZ-IT plans, supplies, connects and operates the agreed environment and documents which external connections exist.
Control your data flows
Local processing is possible, while external integrations, updates and remote access are configured deliberately and documented.
Open stack and defined exit
Proven open-source components, documented configurations and agreed data exports reduce dependency on the operator.
Designed for §203 requirements
For professional secrecy holders, we design data flows, access and technical measures around the use case and accept the required contributing-person obligation where applicable.
Direct entry points into on-premises operations
Configure an App Node, request Section 203 operations or expose internal applications through a gateway.
Configurator
Configure your App Node
Choose storage, access, backup and required applications in the configurator. WZ-IT checks the selection for compatibility and operational boundaries before quoting.
from €349 excl. VAT / month
Plus one-time provisioning and initial setup.
Open the configuratorFor professional secrecy holders
Section 203 managed on premises
Applications, access paths, backup and operating scope are reviewed together and quoted on request.
from €499.90 excl. VAT / month
Final scope and price on request.
Request Section 203 operationsExtension for on premises and hybrid
Expose internal web applications through a managed cloud gateway
WZ-IT operates the upstream reverse-proxy layer with domain, TLS, monitoring and a defined connection path to the target system.
from €129.90 excl. VAT / month
ongoing managed service
View Cloud GatewayManaged open source with consulting and operations
Customer feedback on open-source selection, implementation, maintenance and long-term operations.












“WZ-IT moved our studio infrastructure from decentralised individual devices to a central platform: every site is securely connected via VPN, new devices are onboarded automatically and an entire site is provisioned from a template, without manual steps on location. What impressed me most is the breadth and depth of their knowledge: Timo and Robin are not a typical IT provider who sets up a server and leaves. The two of them think their way into highly complex infrastructure and software topics, work through every requirement we put in front of them, and build networking, provisioning and operations so that everything fits together in the end. WZ-IT is an excellent partner for complex software, network and architecture projects.”

Steve Kirchner
Managing Director, nextGYM GmbH
“Professional, honest and technically thoroughly sound: WZ-IT set up our Proxmox and backup infrastructure securely and future-proof. The consulting from Timo and Robin was objective and needs-driven, the implementation smooth and the final documentation exemplary. You can tell immediately that business-critical infrastructure is thought through holistically from the outset here and implemented with clear ownership.”
Pascal Block
Project Manager, Stadtwerke Brühl GmbH
Stadtwerke Brühl - municipal energy and infrastructure utility.
“Communication with WZ-IT was open, friendly and professional from the very beginning. Mr. Wevelsiep and Mr. Zins responded to every one of our questions patiently, promptly and respectfully, and contributed their own suggestions and good ideas on how to modernize our server infrastructure and adapt it even better to our needs. Throughout, WZ-IT consistently kept our need for data sovereignty and GDPR compliance in mind. Even short-notice adjustments and change requests from our side were implemented quickly and patiently and integrated consistently into the overall concept. From planning to the final handover, every step was documented transparently and comprehensively - so if a provider change should ever become necessary, the documentation would let us onboard a successor into our infrastructure very quickly. We are extremely satisfied with WZ-IT and hope to continue working together for a long time.”
Christoph Mußmann
Project Officer, DGHO e.V.
DGHO - German Society for Hematology and Medical Oncology.

“I got to know Timo and Robin as dedicated and professional partners who make a lot of things possible for their clients that initially seem impossible. I felt very well advised. The services offered have thoroughly convinced me. (translated)”
Andrea Pawlowski
Communications Manager, Golem.de
Golem.de - leading German IT news outlet.
“While looking for a partner to integrate a local AI solution, we came across Timo and Robin - and could not have made a better decision. They quickly understood our requirements and solved technical challenges competently and pragmatically. We were particularly impressed by the straightforward collaboration, their high level of expertise and the speed of implementation. We are delighted to have Timo and Robin at our side as reliable business partners and look forward to our next projects together. (translated)”
Henrik Jeche
Head of IT Administration
ml&s - full-service provider for the electronics industry.

“With Timo and Robin, you're not only on the safe side technically - you also get the best human support! Whether it's quick help in everyday life or complex IT solutions: the guys from WZ-IT think along with you, act quickly and speak a language you understand. The collaboration is uncomplicated, reliable and always on an equal footing. That makes IT fun - and above all: it works! Big thank you to the team! (translated)”
Sonja Aßer
Data Manager, ARGE
ARGE Neue Medien - master data & digital standards for plumbing and building technology.
“I recently worked with Timo and the WZ-IT team, and honestly, it turned out to be one of the best tech decisions I have made for my business. Right from the start, Timo took the time to walk me through every step in a simple and calm way. No matter how many questions I had, he never rushed me. The results speak for themselves. With WZ-IT, we reduced our monthly expenses from $1,300 down to $250. This was a huge win for us.”
Aleksandr Shuliko
CTO, EVA Real Estate
EVA Real Estate - leading real-estate agency in Dubai.

“WZ-IT manages our Proxmox cluster reliably and professionally. The team handles continuous monitoring and regular updates for us and responds very quickly to any issues or inquiries. They also configure new nodes, systems, and applications that we need to add to our cluster. With WZ-IT's proactive support, our cluster and the business-critical applications running on it remain stable, and high availability is consistently ensured. We value the professional collaboration and the noticeable relief it brings to our daily operations.”
Pascal Hakkers
Aphy AG
Aphy AG - AI platform for hotel back-office.

“WZ-IT provided very competent support in implementing our server and virtualization infrastructure. As part of the project, a Proxmox-based virtualization environment was set up along with a virtual machine for our application systems. Additionally, a structured backup concept was implemented. A particular focus was on security: the setup of a VPN tunnel and the clean implementation of encryption and access concepts were professionally executed. The structured consulting as well as the reliable and swift implementation deserve special mention. We are very satisfied with the services provided and are happy to recommend WZ-IT.”
John Hellmerichs
Managing Director, AInergy GmbH
AInergy - consultancy for energy and facility management.

“We have had very good experiences with Mr. Wevelsiep and WZ-IT. The consultation was professional, clearly understandable, and at fair prices. The team not only implemented our requirements but also thought along and proactively. Instead of just processing individual tasks, they provided us with well-founded explanations that strengthened our own understanding. WZ-IT took a lot of pressure off us with their structured approach - that was exactly what we needed and is the reason why we keep coming back. (translated)”
Matthias Zimmermann
Managing Director, Annota GmbH
Annota - healthtech startup with an AI documentation assistant.
“Timo and Robin from WZ-IT set up a RocketChat server for us - and I couldn't be more satisfied! From the initial consultation to the final implementation, everything was absolutely professional, efficient, and to my complete satisfaction. I particularly appreciate the clear communication, transparent pricing, and the comprehensive expertise that both bring to the table. Even after the setup, they take care of the maintenance, which frees up my time enormously and allows me to focus on other important areas of my business - with the good feeling that our IT is in the best hands. I can recommend WZ-IT without reservation and look forward to continuing our collaboration! (translated)”
Sebastian Maier
Managing Director, Yonju GmbH
Yonju - business coaching and AI products.
“Counting on WZ-IT team was crucial, their expertise and solutions gave us the pace to deploy in production our services, even suggesting and performing improvements over our configuration and setup. We expect to keep counting on them for continuous maintenance of our services and implementation of new solutions.”
Gabriel Sanz Señor
Managing Director, Odiseo Solutions
Odiseo Solutions - software engineering for the space industry.


“WZ-IT supported us professionally with the provisioning and setup of NetBird. Alongside the technical implementation, we also received well-founded advice on connecting our Kubernetes clusters. The recommendations were concrete and directly actionable. The collaboration was consistently reliable, fast and on equal terms. We can recommend WZ-IT without reservation.”
Kai Clauß
Head of Development, SweetConnect GmbH
SweetConnect - cross-manufacturer Industry 4.0 platform for confectionery production.

Let's talk about your project - honest and no strings attached
- Straight with Timo and Robin - no sales team, no pitch
- An honest take, including when we are not the right fit
- Concrete next steps for infrastructure, software or AI
No risk: worst case, you leave with a clearer understanding of your project than before.


“WZ-IT's advice on our Azure migration was technically sound and completely non-binding right from the intro call - we took away a great deal.”
Frequently asked questions about on premises and hybrid
Answers to the most important questions
The system is physically located at your organisation or another site you specify. WZ-IT plans, supplies, connects and operates the agreed environment. For the App Node, hardware is provided as part of the managed subscription.
Grammatically correct is "on-premises"; in the IT industry "on-premise" (short "on-prem") has become standard. Both mean the same: the software runs at your site rather than in someone else's cloud.
The App Node costs from €349 excl. VAT / month as a managed subscription, plus one-time provisioning and initial setup. The AI Cube for local AI costs from €6,490 excl. VAT one-time. Section 203 managed on premises for professional secrecy holders costs from €499.90 excl. VAT / month. Final scope and price follow a review of applications, access paths and operating scope.
Sensitive data and functions stay local while approved services from the cloud or a data centre remain available. In return there are more transitions between network, identities and data paths that must be planned, secured and operated. The target architecture therefore defines which connections exist and who operates them.
No. Local and external systems can be combined deliberately. The target architecture defines which data and functions remain local and which approved external services are accessible.
Depending on requirements, access uses NetBird, WireGuard, an existing corporate VPN or a secured reverse-proxy gateway. The node does not need an exposed administration interface or necessarily a public IP.
No. Storage location alone does not answer every data protection question; access, backups, remote maintenance, endpoints and connected services matter as well. WZ-IT designs and documents these data flows, while legal evaluation of the specific use remains with the controller.
The architecture can be designed for professional secrecy holders. This includes documented data flows, access controls and, where applicable, our written confidentiality obligation as a contributing person. Section 203 and GDPR require separate assessment; legal evaluation of the specific use remains with the controller and its advisers.
Request on-premises or hybrid infrastructure
Describe the site, applications, data volume and required operating scope. WZ-IT reviews the hardware, architecture and secure network integration.
Let's Talk About Your Idea
Whether a specific IT challenge or just an idea - we look forward to the exchange. In a brief conversation, we'll evaluate together if and how your project fits with WZ-IT.
Arrange a callback
Companies worldwide trust WZ-IT