


25.06.2026
Local AI for Tax Firms: §203, Client Data and RAG
How tax firms can process documents, correspondence and internal knowledge with local AI.
#AI#TaxAdvisors#DataProtection
Read More

Client emails, receipts and payroll data are sensitive. We set up a local AI platform with controlled data sources, roles and documented access paths.
Companies worldwide trust WZ-IT
Sorting, assigning and preparing client emails and incoming receipts takes time. When AI is used, the resulting data paths must be deliberately limited.
A DPA with a cloud provider does not define how data flows, source permissions and §203 are implemented technically.
Client data is among the most sensitive data there is - a leak becomes a matter for professional supervision and costs trust you cannot win back.
We configure and operate AI Cube for the agreed GDPR and Section 203 scope. This includes controlled data paths, limited permissions, documented maintenance, the appropriate DPA and written secrecy obligations for the people involved. Legal evaluation of the specific use remains with the controller and its advisers.
§203 StGB protects confidential information entrusted by clients, patients and other parties. The necessary involvement of contributing persons is permitted. What matters is that access is limited to what is necessary, the people involved are bound to secrecy and the complete data and maintenance path is controlled.
With public AI services, inputs and documents leave your own infrastructure. Whether a service is suitable in a specific case therefore depends not only on a DPA, but also on data flows, subprocessors, access permissions and the actual use.
On-premises inference, local vector search and internally operated interfaces keep technical processing in your controlled environment. This reduces external data paths and subprocessors and allows access to be limited precisely.
When we provide setup or operations as a contributing person, the people involved accept a written secrecy obligation and are instructed about the criminal consequences. Where personal data is involved, this is combined with a DPA, limited administrative rights and documented maintenance paths.
These technical and contractual building blocks form part of the agreed §203 scope:
Data-protection layer
Secrecy and instruction on criminal consequences
necessary rights, logging and controlled paths
This content is general information and not legal or tax advice. The specific implementation under §203 must be reviewed professionally on a case-by-case basis.
Staff receive a familiar AI chat with local models and dedicated knowledge areas. DATEV connections, document workflows and automated RAG pipelines are planned as a separate integration scope.
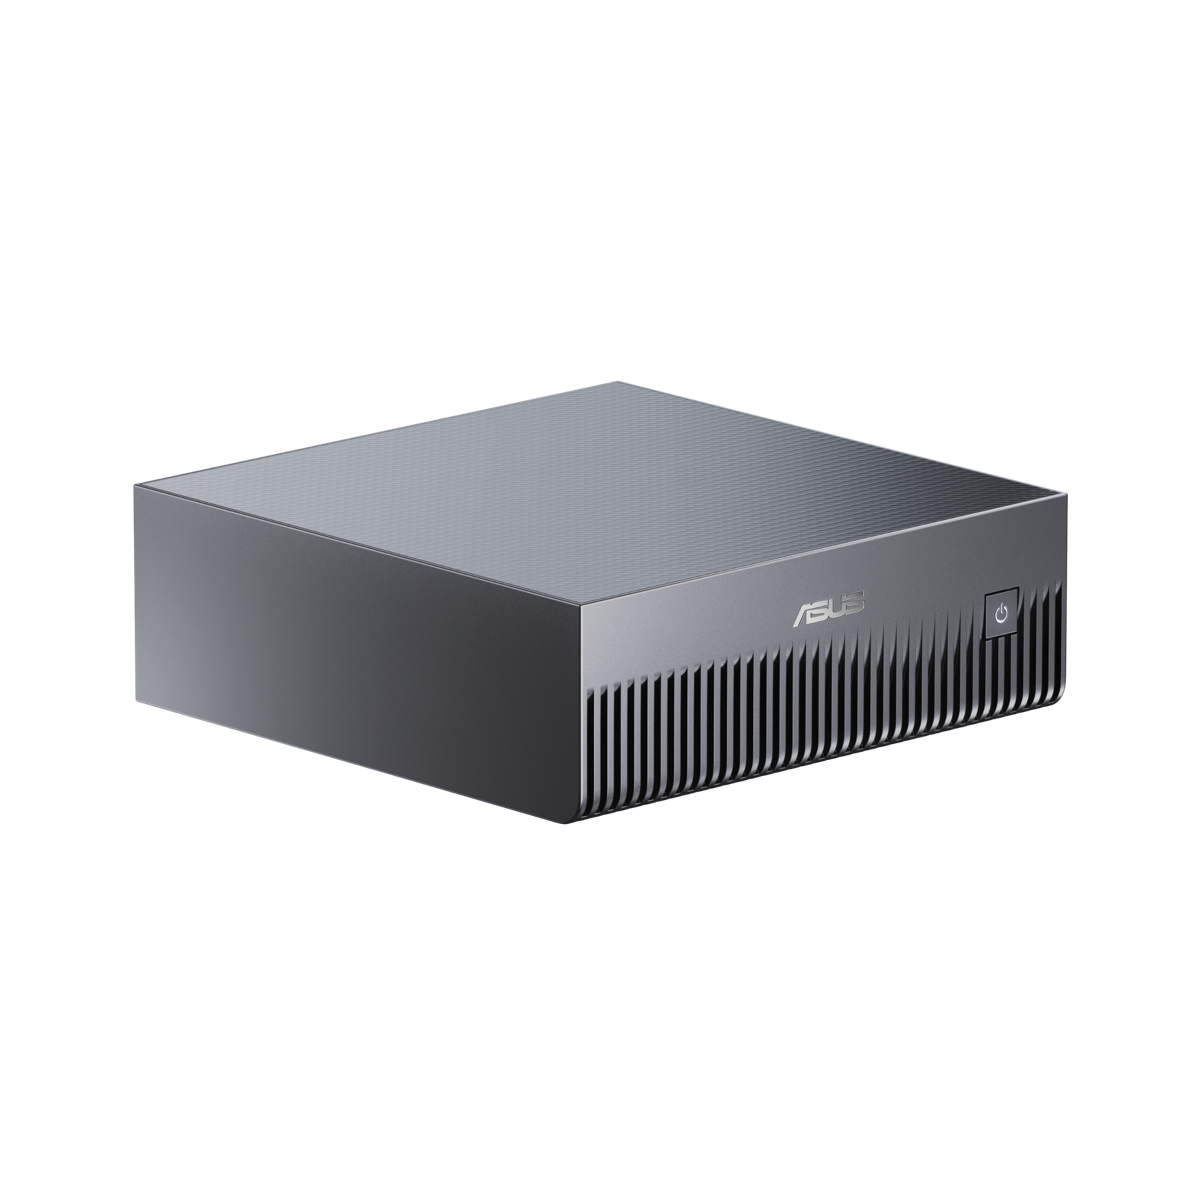
Delivered ready to use within 10 working days
€6,490 excl. VAT one-time
Device, setup, briefing and shipping
€349.90 excl. VAT / month
AI Cube Care · first year accompanied, then cancellable monthly
RAG, data sources, integrations, secure connectivity and custom workflows are scoped separately.
AI Cube Care keeps the device running: a monthly maintenance window, tested model updates with a rollback path, round-the-clock monitoring, ticket support and warranty handling. For confidentiality professionals we add a data processing agreement under Art. 28 GDPR and the written secrecy obligation under Section 203 (4) of the German Criminal Code, including instruction on the criminal consequences; on request remote access stays switched off by default.
These examples describe possible workflows. Data sources, permissions and professional review are defined for the concrete use case.
Sovereign AI is a lifecycle, not a device purchase - and everything stays on your infrastructure.
Workshop, sizing, data classification and §203 contract framework. We understand your stack, professional software and compliance requirements before we recommend.
On-premise build on your hardware, RAG on your documents with access control, integration into your professional software, secrecy obligation + DPA.
Updates, monitoring, model upgrades and RAG maintenance as a service contract - or you operate fully yourself. Handover and knowledge transfer included.
From hardware and inference through RAG and integration to operations and security - no interface ping-pong between advice, build and operations.
Enquiry
Describe the workflow and data that should be processed locally or in a controlled environment.
From local AI integration to architecture, data sovereignty and ongoing operations.










“WZ-IT moved our studio infrastructure from decentralised individual devices to a central platform: every site is securely connected via VPN, new devices are onboarded automatically and an entire site is provisioned from a template, without manual steps on location. What impressed me most is the breadth and depth of their knowledge: Timo and Robin are not a typical IT provider who sets up a server and leaves. The two of them think their way into highly complex infrastructure and software topics, work through every requirement we put in front of them, and build networking, provisioning and operations so that everything fits together in the end. WZ-IT is an excellent partner for complex software, network and architecture projects.”
Steve Kirchner
Managing Director, nextGYM GmbH
“While looking for a partner to integrate a local AI solution, we came across Timo and Robin - and could not have made a better decision. They quickly understood our requirements and solved technical challenges competently and pragmatically. We were particularly impressed by the straightforward collaboration, their high level of expertise and the speed of implementation. We are delighted to have Timo and Robin at our side as reliable business partners and look forward to our next projects together. (translated)”
Henrik Jeche
Head of IT Administration
ml&s - full-service provider for the electronics industry.

“Communication with WZ-IT was open, friendly and professional from the very beginning. Mr. Wevelsiep and Mr. Zins responded to every one of our questions patiently, promptly and respectfully, and contributed their own suggestions and good ideas on how to modernize our server infrastructure and adapt it even better to our needs. Throughout, WZ-IT consistently kept our need for data sovereignty and GDPR compliance in mind. Even short-notice adjustments and change requests from our side were implemented quickly and patiently and integrated consistently into the overall concept. From planning to the final handover, every step was documented transparently and comprehensively - so if a provider change should ever become necessary, the documentation would let us onboard a successor into our infrastructure very quickly. We are extremely satisfied with WZ-IT and hope to continue working together for a long time.”
Christoph Mußmann
Project Officer, DGHO e.V.
DGHO - German Society for Hematology and Medical Oncology.
“We have had very good experiences with Mr. Wevelsiep and WZ-IT. The consultation was professional, clearly understandable, and at fair prices. The team not only implemented our requirements but also thought along and proactively. Instead of just processing individual tasks, they provided us with well-founded explanations that strengthened our own understanding. WZ-IT took a lot of pressure off us with their structured approach - that was exactly what we needed and is the reason why we keep coming back. (translated)”
Matthias Zimmermann
Managing Director, Annota GmbH
Annota - healthtech startup with an AI documentation assistant.
“I got to know Timo and Robin as dedicated and professional partners who make a lot of things possible for their clients that initially seem impossible. I felt very well advised. The services offered have thoroughly convinced me. (translated)”
Andrea Pawlowski
Communications Manager, Golem.de
Golem.de - leading German IT news outlet.
“Professional, honest and technically thoroughly sound: WZ-IT set up our Proxmox and backup infrastructure securely and future-proof. The consulting from Timo and Robin was objective and needs-driven, the implementation smooth and the final documentation exemplary. You can tell immediately that business-critical infrastructure is thought through holistically from the outset here and implemented with clear ownership.”
Pascal Block
Project Manager, Stadtwerke Brühl GmbH
Stadtwerke Brühl - municipal energy and infrastructure utility.
“With Timo and Robin, you're not only on the safe side technically - you also get the best human support! Whether it's quick help in everyday life or complex IT solutions: the guys from WZ-IT think along with you, act quickly and speak a language you understand. The collaboration is uncomplicated, reliable and always on an equal footing. That makes IT fun - and above all: it works! Big thank you to the team! (translated)”
Sonja Aßer
Data Manager, ARGE
ARGE Neue Medien - master data & digital standards for plumbing and building technology.
“I recently worked with Timo and the WZ-IT team, and honestly, it turned out to be one of the best tech decisions I have made for my business. Right from the start, Timo took the time to walk me through every step in a simple and calm way. No matter how many questions I had, he never rushed me. The results speak for themselves. With WZ-IT, we reduced our monthly expenses from $1,300 down to $250. This was a huge win for us.”
Aleksandr Shuliko
CTO, EVA Real Estate
EVA Real Estate - leading real-estate agency in Dubai.

“WZ-IT manages our Proxmox cluster reliably and professionally. The team handles continuous monitoring and regular updates for us and responds very quickly to any issues or inquiries. They also configure new nodes, systems, and applications that we need to add to our cluster. With WZ-IT's proactive support, our cluster and the business-critical applications running on it remain stable, and high availability is consistently ensured. We value the professional collaboration and the noticeable relief it brings to our daily operations.”
Pascal Hakkers
Aphy AG
Aphy AG - AI platform for hotel back-office.

“WZ-IT provided very competent support in implementing our server and virtualization infrastructure. As part of the project, a Proxmox-based virtualization environment was set up along with a virtual machine for our application systems. Additionally, a structured backup concept was implemented. A particular focus was on security: the setup of a VPN tunnel and the clean implementation of encryption and access concepts were professionally executed. The structured consulting as well as the reliable and swift implementation deserve special mention. We are very satisfied with the services provided and are happy to recommend WZ-IT.”
John Hellmerichs
Managing Director, AInergy GmbH
AInergy - consultancy for energy and facility management.
“Timo and Robin from WZ-IT set up a RocketChat server for us - and I couldn't be more satisfied! From the initial consultation to the final implementation, everything was absolutely professional, efficient, and to my complete satisfaction. I particularly appreciate the clear communication, transparent pricing, and the comprehensive expertise that both bring to the table. Even after the setup, they take care of the maintenance, which frees up my time enormously and allows me to focus on other important areas of my business - with the good feeling that our IT is in the best hands. I can recommend WZ-IT without reservation and look forward to continuing our collaboration! (translated)”
Sebastian Maier
Managing Director, Yonju GmbH
Yonju - business coaching and AI products.

“Counting on WZ-IT team was crucial, their expertise and solutions gave us the pace to deploy in production our services, even suggesting and performing improvements over our configuration and setup. We expect to keep counting on them for continuous maintenance of our services and implementation of new solutions.”
Gabriel Sanz Señor
Managing Director, Odiseo Solutions
Odiseo Solutions - software engineering for the space industry.
“WZ-IT supported us professionally with the provisioning and setup of NetBird. Alongside the technical implementation, we also received well-founded advice on connecting our Kubernetes clusters. The recommendations were concrete and directly actionable. The collaboration was consistently reliable, fast and on equal terms. We can recommend WZ-IT without reservation.”
Kai Clauß
Head of Development, SweetConnect GmbH
SweetConnect - cross-manufacturer Industry 4.0 platform for confectionery production.

Whether a specific IT challenge or just an idea - we look forward to the exchange. In a brief conversation, we'll evaluate together if and how your project fits with WZ-IT.
Companies worldwide trust WZ-IT




No risk: worst case, you leave with a clearer understanding of your project than before.
“WZ-IT's advice on our Azure migration was technically sound and completely non-binding right from the intro call - we took away a great deal.”