

Support wanted for your cloud infrastructure? WZ-IT takes over consulting, conception, setup, operation, support and monitoring of your infrastructure.
Arrange a free appointment now
CrowdSec is a free, open-source intrusion prevention system (IPS) that analyzes suspicious activity on your servers and automatically blocks attackers. The special feature: All users share anonymized attack signatures with each other - creating a global threat database in real time that offers protection through swarm intelligence.
Table of Contents
- Why CrowdSec and not Fail2Ban?
- Architecture at a glance
- Installation in 5 minutes (Debian/Ubuntu)
- Set up CrowdSec console
- Conclusion
Why CrowdSec and not Fail2Ban?
| Criterion | CrowdSec | Fail2Ban |
|---|---|---|
| Community Shield | Yes, shared blocklists worldwide | No |
| Multi-layered | Agent + flexible bouncers | iptables/jail only |
| Web dashboard | CrowdSec Console or Grafana | No |
| Scenario language | YAML-based patterns (simple) | Regex-based filters |
| Ecosystem | > 25 bouncers (Nginx, Cloudflare ... ) | Limited actions |
Architecture at a glance
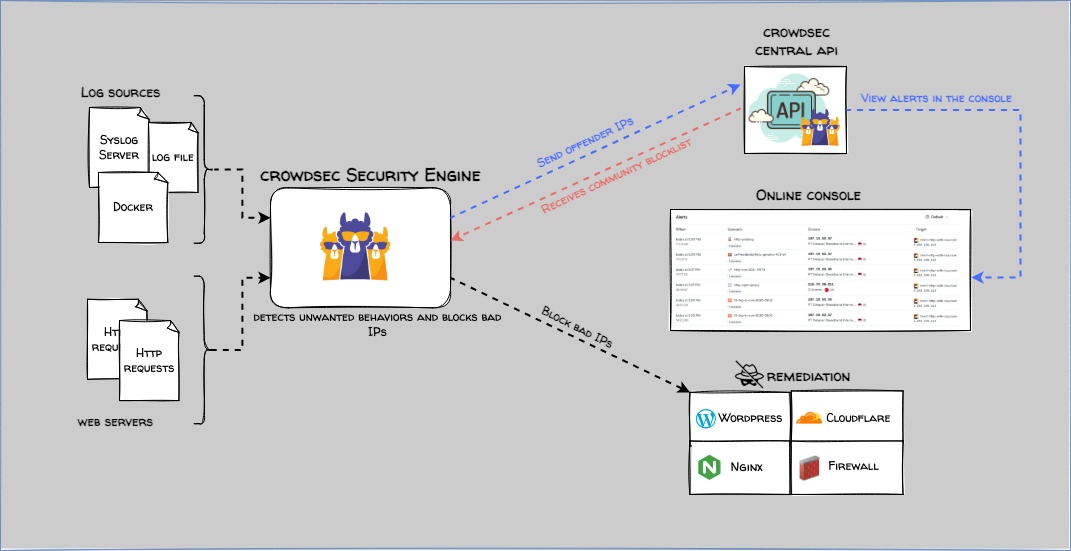
CrowdSec consists of the security engine that runs on your servers and the optional web-based CrowdSec Console, which visualizes the collected data. The former local Metabase dashboard (cscli dashboard) was removed with CrowdSec v1.7.0 in September 2025; as an alternative to the Console, the engine's Prometheus metrics can be visualized in Grafana. As of October 2026, v1.8.1 is the current version. The engine analyzes log files in real time and detects suspicious patterns. In the event of an
attack, the attacker is automatically blocked and the signature is transmitted to the CrowdSec community.
Installation in 5 minutes (Debian/Ubuntu)
# Add repository
curl -s https://install.crowdsec.net | sudo sh
# Install security engine
sudo apt install crowdsec
# Install iptables bouncer
sudo apt install crowdsec-firewall-bouncer-iptables
# Restart CrowdSec engine
sudo service crowdsec restart
The first command downloads the repository script from install.crowdsec.net and runs it as root. To review it first, save it with curl -fsSL https://install.crowdsec.net -o crowdsec-install.sh, read it, and then run it with sudo sh crowdsec-install.sh. The repository can also be added manually (installation guide).
Set up CrowdSec console
Since we have already installed CrowdSec, we scroll down in the Console and copy the installation command for the console.

We paste this into our terminal and execute it:
sudo cscli console enroll -e context cmbwirxts0003l508ooeg42mq
Now we need to confirm the enrollment in the CrowdSec console. To do this, we go to the CrowdSec console and click on "Enrollments". If we refresh the page, we will see the following:
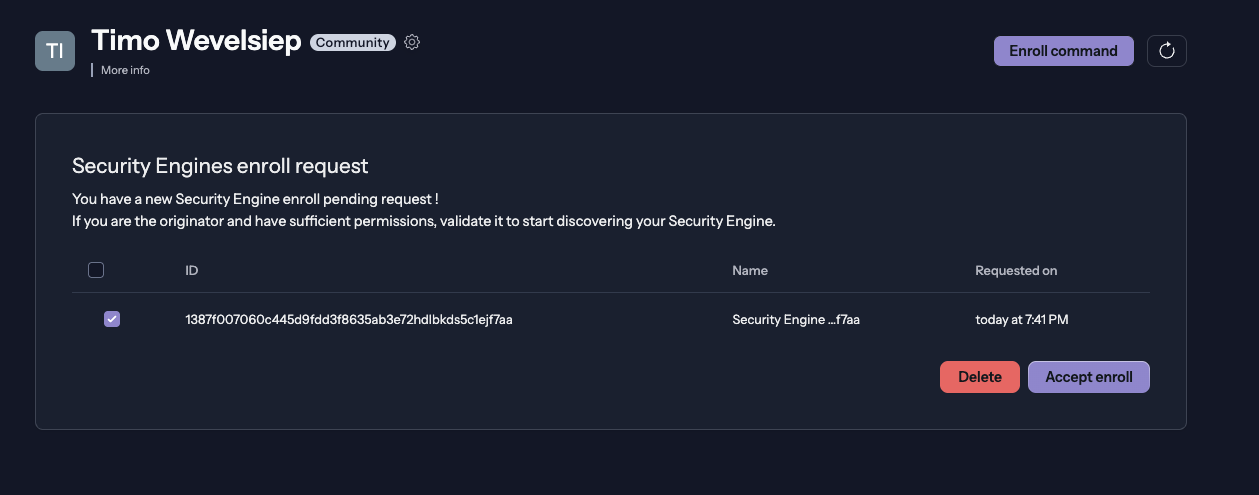 Now we restart the CrowdSec engine so that the configuration is applied:
sudo service crowdsec restart
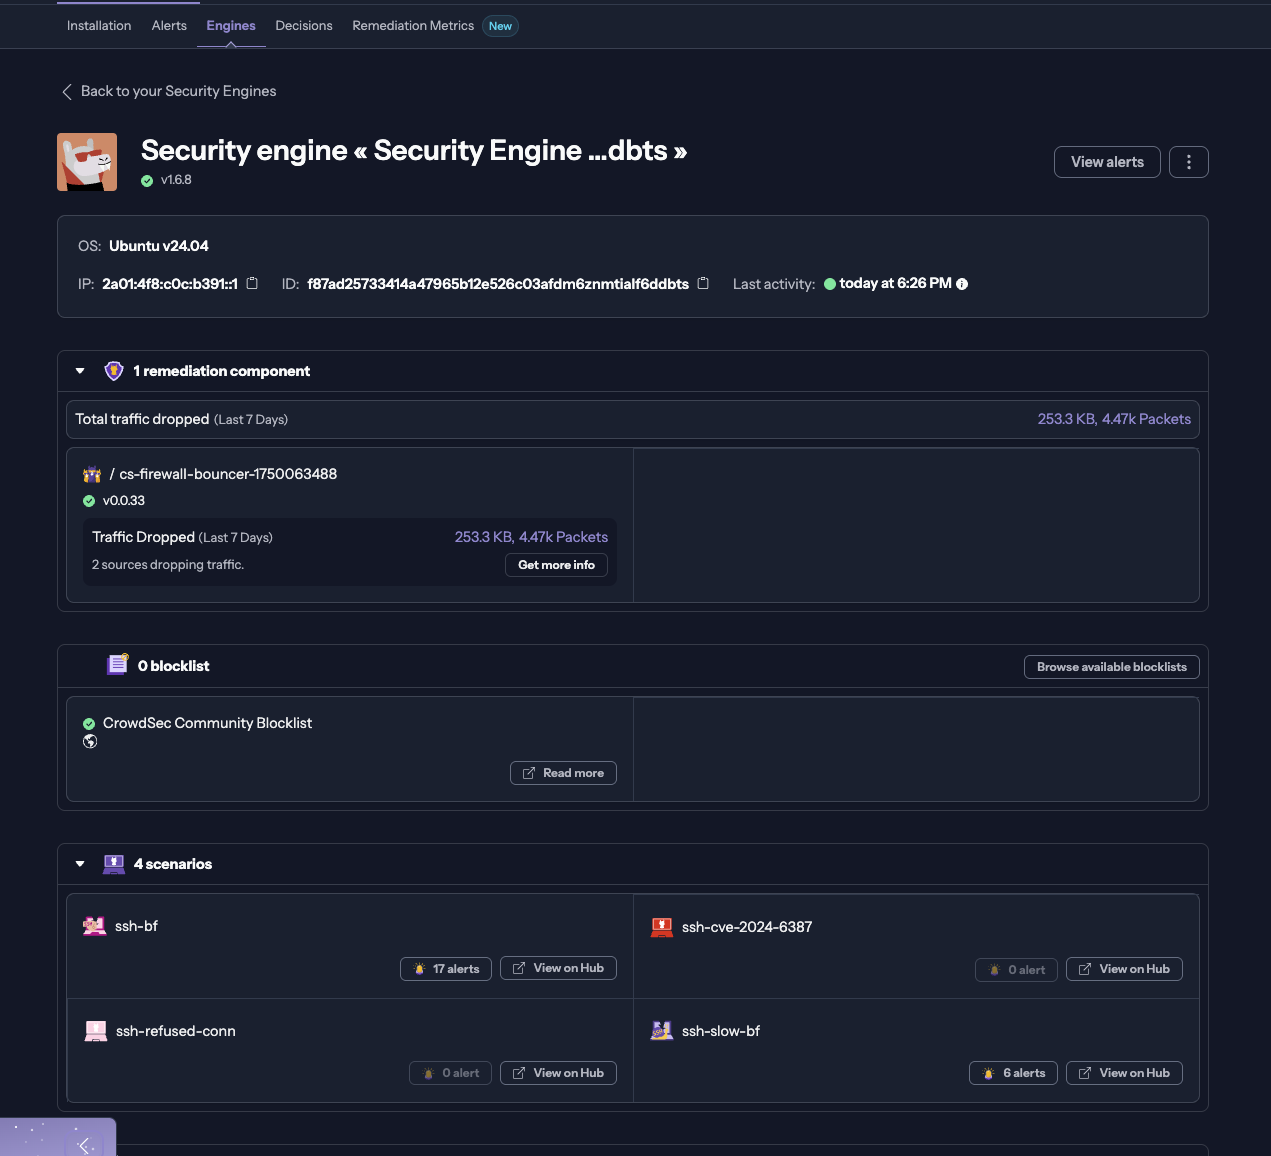
We now see our security engine in the CrowdSec console and can view the collected data.
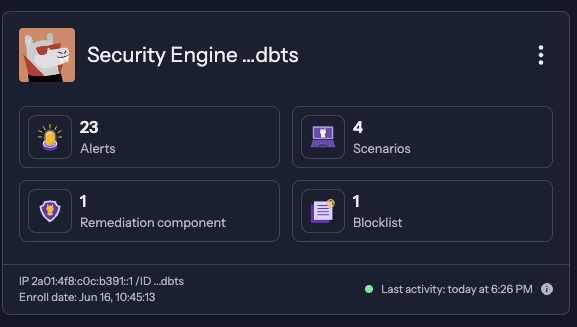
We can also see how attacks have already been detected and blocked:
Still unsure which tool fits? The Linux server audit checks patch level, access, firewall and backups of your server and prioritises the measures, from €290 excl. VAT.
Conclusion
We have now successfully installed and configured CrowdSec. The engine now analyzes the log files in real time and automatically blocks attackers via the iptables bouncer. Thanks to the integration into the CrowdSec community, we benefit from a global threat database that is constantly updated.
A list of available bouncers can be found here.
























