
Asset and licence data
Fields, asset tags, status models, locations and lifecycles are structured to fit existing inventories.


We implement and operate Snipe-IT as a central IT asset platform - including data migration, roles, LDAP or SAML, integrations, backups and documented operating processes.
Companies worldwide trust WZ-IT
The following are trademarks of their respective owners: Snipe-IT (Grokability, Inc.). WZ-IT is an independent service provider and has no business, partnership, or contractual relationship with these companies. We offer independent migration, installation, hosting, and operations services.
Snipe-IT manages devices, accessories, components, consumables and software licences. Check-in and checkout show who an item is assigned to, while unique asset tags and labels support physical inventory work.
WZ-IT connects the application to directories, existing inventory sources and support processes. We separate technical availability from data quality: ownership, locations, asset classes and lifecycle rules must be defined with the responsible teams.
We clean and map existing CSV or system exports, test the import with a representative subset and document mandatory fields, asset tags, states and assignments before the production cutover.
Snipe-IT does not include its own automatic network discovery agent. Where suitable interfaces exist, we connect current discovery, MDM or inventory systems through the API and controlled synchronisation jobs.
An IT asset system is only as reliable as its data model, processes and operations. We combine Snipe-IT, its database, file storage, identity, imports and backups with clear responsibilities.
Fields, asset tags, status models, locations and lifecycles are structured to fit existing inventories.
CSV, REST API, LDAP, SAML and SCIM are connected through controlled processes instead of overwriting data blindly.
Permissions, checkout, check-in, inventory and approvals are aligned with the responsible teams.
Monitoring, updates, database and file backups plus restore tests protect the technical platform.
We separate technical platform operations from business responsibility for asset data and processes.
| Area | Responsibility | Scope and boundaries |
|---|---|---|
| Architecture and provisioning | WZ-IT | Web application, MySQL or MariaDB, email, TLS, storage and reproducible deployment. |
| Snipe-IT runtime and updates | WZ-IT | Maintenance of the agreed instance including backup, release assessment and controlled updates. |
| Monitoring and backups | WZ-IT | Monitoring and backup of database, uploads, private attachments and relevant configuration. |
| Data model and initial import | Shared | WZ-IT maps and validates data; the customer confirms fields, states, assignments and authoritative systems. |
| Identity and user synchronisation | Shared | WZ-IT implements LDAP, SAML or SCIM; the customer defines groups, permissions and source systems. |
| Inventory and data maintenance | Customer | Completeness, physical verification, checkout, check-in and business accuracy remain customer processes. |
| Discovery and helpdesk integration | Optional WZ-IT service | Connections to existing MDM, discovery, ticketing or procurement systems are specified separately. |
Manage devices with asset tag, serial number, model, status, location, cost and lifecycle information in a structured register.
Assign assets, accessories and licences to people or locations, return them and retain a traceable assignment history.
Track licence inventory, seats, assignments, terms and procurement information together with associated assets.
Generate labels with QR codes or barcodes and open asset records directly during inventory and service work.
Synchronise or authenticate users through LDAP and, depending on the target system, integrate SAML for login or SCIM for provisioning.
Import inventory data through CSV or the REST API and connect Snipe-IT to MDM, discovery, helpdesk or procurement processes.
A clearly defined operating scope instead of an opaque hosting flat fee.
We set up a test instance for you, usually on the next business day. No payment details required. After seven days it is deleted unless you continue.
Compute, applications, storage and response are shown separately. You can see what ongoing operations include and which requirements need a technical assessment.
We also design custom Snipe-IT architectures, integrations and migrations. Contact us for a technical assessment.
One managed standard Snipe-IT application is included in the Starter workload. Business and higher levels add a flexible operations allowance for planned work during regular service hours. Select compute, additional applications, storage and the appropriate service level.
A workload is one compute instance with the applications agreed for it.
One standard app per workload is already included. Additional dedicated servers count as separate workloads.
€7.99 excl. VAT per additional 100 GB per month, including daily encrypted offsite backup with 7-day retention. Billing is based on provisioned capacity, not actual usage.
We also implement custom backup schedules and retention periods. For example: daily backups retained for 30 days and one monthly backup retained for 12 months. Scope, storage requirements and additional costs are agreed separately.
+€299 excluding VAT per workload and month
Standard hosting runs on a single instance without high availability. Availability for custom architectures is agreed separately.
Zero downtime on request
Distributed operation with several instances, a database cluster and rolling updates, so that a node failure causes no interruption. Only for applications suited to it; design and price after technical assessment.
This page covers installation and the agreed platform operations for Snipe-IT. Custom code, the access layer and special confidentiality requirements remain clearly separated responsibilities that can be added when needed.
Maintain the application
Keep custom extensions, interfaces and dependencies controlled, updated and supportable.
from €699.90 excl. VAT / month
View serviceSecure access
Add identity-based access and private network paths as a separate operational layer.
from €349.90 excl. VAT / month
View serviceOperate confidentially
For professional secrecy holders, define contractual, access and infrastructure requirements in a dedicated operating model.
from €499.90 excl. VAT / month
View serviceThree relevant adjacent paths instead of a long list of further products.
All prices are net and exclude statutory VAT. The offers are addressed to businesses.
View the overall systemEnquiry
Briefly describe the current state and objective for Snipe-IT. We assess infrastructure, integration, and ongoing operations.
Asset count is only one factor. Concurrent users, images and attachments, imports, API synchronisations and reports affect compute, database and storage.
| Usage scenario | Technical starting point | Key factors |
|---|---|---|
| Small inventory with few administrators | S or M, MariaDB | A suitable starting point with moderate attachments and infrequent imports. |
| Several locations or regular inventory work | M or L, separate database and file backups | Data volume, label generation, reports and access peaks are assessed. |
| Regular API, LDAP or SCIM synchronisation | M or L plus planned jobs | Intervals, direction of change, conflicts and rate limits must be defined in advance. |
| Central asset register for several organisational units | Custom architecture | Roles, separation, data quality, recovery targets and integrations determine the target design. |
Data cleansing, initial import, label design and custom integrations are project services and are not included in the generic workload price.
The standard workload covers one managed instance. Migration, large file inventories and complex synchronisation are assessed separately.
Dedicated workload with agreed compute, backup, monitoring and service level.
Operation in your cloud when directories or source systems are directly reachable there.
Integration with existing server, network, email and backup infrastructure.
Snipe-IT connects to directory, MDM, discovery or helpdesk through defined private links.
Snipe-IT contains personally attributable assignments and inventory data. Access, synchronisation, attachments and authoritative systems are therefore documented together.
Administrators, helpdesk, inventory work, CSV imports, MDM, discovery and procurement systems.
TLS, reverse proxy, network rules and optional private access through NetBird or VPN.
Local roles plus LDAP, SAML or SCIM with aligned attributes and permissions.
Assets, licences, accessories, components, consumables, assignments and history.
Structured asset, user, licence and history information.
Images, models, signatures and documents included in backup and recovery.
Controlled data flows to directory, MDM, discovery, helpdesk and other systems.
Before production launch, we jointly define authoritative systems, conflict rules, mandatory fields, permissions and recovery.
Answers about licensing, migration, discovery, identity and operations.
Yes. Snipe-IT is released under GNU AGPL v3. WZ-IT is an independent service provider offering installation, integration and operations; the vendor's commercial offers are separate.
No. Snipe-IT does not include its own network discovery agent (vendor FAQ). Existing MDM, discovery or inventory systems can be connected through the REST API where suitable interfaces exist.
Yes. We clean and map the data, verify unique asset tags and mandatory fields and test the import with a subset. The customer confirms business accuracy and completeness.
Snipe-IT documents LDAP synchronisation and login, SAML authentication and SCIM provisioning. We verify the specific combination with your identity provider and test attribute and deactivation behaviour before rollout.
In addition to the MySQL or MariaDB database, public uploads, private attachments and relevant configuration must be included. We automate protection and test recovery for the agreed setup.
No. The platform supports unique tags, assignments and history but does not replace ownership for inventory, checkout, check-in and data maintenance. We define these processes with the responsible teams.
Yes, provided the participating systems offer suitable APIs or exports. Data direction, authoritative system, conflict rules, error handling and permissions are defined before implementation.
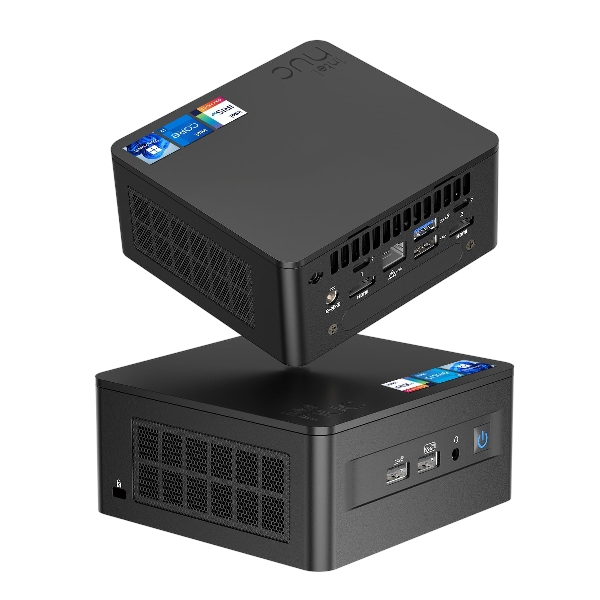
As an alternative to managed hosting in the data centre, WZ-IT provides the hardware, configures Snipe-IT, and handles hardening, monitoring, updates, backup and technical support. Access can be limited to the internal network or enabled through VPN and existing identities.
from EUR 349 excl. VAT / month · plus one-time provisioning and initial setup
These solutions are often used together with Snipe-IT
These solutions offer similar functionalities and can be evaluated together
No risk: worst case, you leave with a clearer understanding of your project than before.
“WZ-IT's advice on our Azure migration was technically sound and completely non-binding right from the intro call - we took away a great deal.”









“WZ-IT moved our studio infrastructure from decentralised individual devices to a central platform: every site is securely connected via VPN, new devices are onboarded automatically and an entire site is provisioned from a template, without manual steps on location. What impressed me most is the breadth and depth of their knowledge: Timo and Robin are not a typical IT provider who sets up a server and leaves. The two of them think their way into highly complex infrastructure and software topics, work through every requirement we put in front of them, and build networking, provisioning and operations so that everything fits together in the end. WZ-IT is an excellent partner for complex software, network and architecture projects.”
Steve Kirchner
Managing Director, nextGYM GmbH
“Professional, honest and technically thoroughly sound: WZ-IT set up our Proxmox and backup infrastructure securely and future-proof. The consulting from Timo and Robin was objective and needs-driven, the implementation smooth and the final documentation exemplary. You can tell immediately that business-critical infrastructure is thought through holistically from the outset here and implemented with clear ownership.”
Pascal Block
Project Manager, Stadtwerke Brühl GmbH
Stadtwerke Brühl - municipal energy and infrastructure utility.
“Communication with WZ-IT was open, friendly and professional from the very beginning. Mr. Wevelsiep and Mr. Zins responded to every one of our questions patiently, promptly and respectfully, and contributed their own suggestions and good ideas on how to modernize our server infrastructure and adapt it even better to our needs. Throughout, WZ-IT consistently kept our need for data sovereignty and GDPR compliance in mind. Even short-notice adjustments and change requests from our side were implemented quickly and patiently and integrated consistently into the overall concept. From planning to the final handover, every step was documented transparently and comprehensively - so if a provider change should ever become necessary, the documentation would let us onboard a successor into our infrastructure very quickly. We are extremely satisfied with WZ-IT and hope to continue working together for a long time.”
Christoph Mußmann
Project Officer, DGHO e.V.
DGHO - German Society for Hematology and Medical Oncology.
“I got to know Timo and Robin as dedicated and professional partners who make a lot of things possible for their clients that initially seem impossible. I felt very well advised. The services offered have thoroughly convinced me. (translated)”
Andrea Pawlowski
Communications Manager, Golem.de
Golem.de - leading German IT news outlet.

“While looking for a partner to integrate a local AI solution, we came across Timo and Robin - and could not have made a better decision. They quickly understood our requirements and solved technical challenges competently and pragmatically. We were particularly impressed by the straightforward collaboration, their high level of expertise and the speed of implementation. We are delighted to have Timo and Robin at our side as reliable business partners and look forward to our next projects together. (translated)”
Henrik Jeche
Head of IT Administration
ml&s - full-service provider for the electronics industry.

“With Timo and Robin, you're not only on the safe side technically - you also get the best human support! Whether it's quick help in everyday life or complex IT solutions: the guys from WZ-IT think along with you, act quickly and speak a language you understand. The collaboration is uncomplicated, reliable and always on an equal footing. That makes IT fun - and above all: it works! Big thank you to the team! (translated)”
Sonja Aßer
Data Manager, ARGE
ARGE Neue Medien - master data & digital standards for plumbing and building technology.
“I recently worked with Timo and the WZ-IT team, and honestly, it turned out to be one of the best tech decisions I have made for my business. Right from the start, Timo took the time to walk me through every step in a simple and calm way. No matter how many questions I had, he never rushed me. The results speak for themselves. With WZ-IT, we reduced our monthly expenses from $1,300 down to $250. This was a huge win for us.”
Aleksandr Shuliko
CTO, EVA Real Estate
EVA Real Estate - leading real-estate agency in Dubai.

“WZ-IT manages our Proxmox cluster reliably and professionally. The team handles continuous monitoring and regular updates for us and responds very quickly to any issues or inquiries. They also configure new nodes, systems, and applications that we need to add to our cluster. With WZ-IT's proactive support, our cluster and the business-critical applications running on it remain stable, and high availability is consistently ensured. We value the professional collaboration and the noticeable relief it brings to our daily operations.”
Pascal Hakkers
Aphy AG
Aphy AG - AI platform for hotel back-office.

“WZ-IT provided very competent support in implementing our server and virtualization infrastructure. As part of the project, a Proxmox-based virtualization environment was set up along with a virtual machine for our application systems. Additionally, a structured backup concept was implemented. A particular focus was on security: the setup of a VPN tunnel and the clean implementation of encryption and access concepts were professionally executed. The structured consulting as well as the reliable and swift implementation deserve special mention. We are very satisfied with the services provided and are happy to recommend WZ-IT.”
John Hellmerichs
Managing Director, AInergy GmbH
AInergy - consultancy for energy and facility management.
“We have had very good experiences with Mr. Wevelsiep and WZ-IT. The consultation was professional, clearly understandable, and at fair prices. The team not only implemented our requirements but also thought along and proactively. Instead of just processing individual tasks, they provided us with well-founded explanations that strengthened our own understanding. WZ-IT took a lot of pressure off us with their structured approach - that was exactly what we needed and is the reason why we keep coming back. (translated)”
Matthias Zimmermann
Managing Director, Annota GmbH
Annota - healthtech startup with an AI documentation assistant.
“Timo and Robin from WZ-IT set up a RocketChat server for us - and I couldn't be more satisfied! From the initial consultation to the final implementation, everything was absolutely professional, efficient, and to my complete satisfaction. I particularly appreciate the clear communication, transparent pricing, and the comprehensive expertise that both bring to the table. Even after the setup, they take care of the maintenance, which frees up my time enormously and allows me to focus on other important areas of my business - with the good feeling that our IT is in the best hands. I can recommend WZ-IT without reservation and look forward to continuing our collaboration! (translated)”
Sebastian Maier
Managing Director, Yonju GmbH
Yonju - business coaching and AI products.

“Counting on WZ-IT team was crucial, their expertise and solutions gave us the pace to deploy in production our services, even suggesting and performing improvements over our configuration and setup. We expect to keep counting on them for continuous maintenance of our services and implementation of new solutions.”
Gabriel Sanz Señor
Managing Director, Odiseo Solutions
Odiseo Solutions - software engineering for the space industry.
“WZ-IT supported us professionally with the provisioning and setup of NetBird. Alongside the technical implementation, we also received well-founded advice on connecting our Kubernetes clusters. The recommendations were concrete and directly actionable. The collaboration was consistently reliable, fast and on equal terms. We can recommend WZ-IT without reservation.”
Kai Clauß
Head of Development, SweetConnect GmbH
SweetConnect - cross-manufacturer Industry 4.0 platform for confectionery production.

Whether a specific IT challenge or just an idea - we look forward to the exchange. In a brief conversation, we'll evaluate together if and how your project fits with WZ-IT.
Companies worldwide trust WZ-IT


